
Policy enforcement has moved to the forefront. Let’s break down why this is the case and how policies can help you improve governance as you stay in control of operations.
First, let’s examine your current production environment. Compliance, governance, and security aligned with specific standards represent an ongoing and essential need. In fact, some standards come with costly daily fines for each day an environment is out of compliance. Furthermore, standards constantly evolve, with new rules requiring more rigorous actions. For example, Secure Sockets Layer/Transport Layer Security (SSL/TLS) certificates now have shorter lifespans, impacting standards that require valid certificates.
If you have an enterprise-scale environment, compliance demand expands in both scale and scope. Automation can help reduce this burden by providing continuous visibility into the state of the environment measured by those standards. Note that some audits require specific tools and audit trails to collect evidence, and I'll show how to get compliant and stay that way.
Now, let’s add AI into this picture. You may need to demonstrate data lineage, protect data and privacy, document a complete inventory of your AI systems, provide audit trails of every action your AI systems have taken, demonstrate control over AI systems, and so on. Automation across your existing solutions and new AI capabilities is the way to manage it all at scale—with speed, consistency, and accuracy. This is why organizations are turning to policy as code.
What is policy as code?
Policy as code uses defined policies to evaluate technology code throughout the entire release process to:
- Apply compliance, security, and internal standards consistently to code as it moves through each lifecycle step from the start (for example, checking into the repository) to running in production
- Control what automation can do—for example, who (or what AI) can operate on which set of inventory and tasks, and at what level of authority
- Capture audit trails of every action taken by automation
- Employ controls like role-based access control (RBAC)
- Protect sensitive data and systems using secrets management
Red Hat Ansible Automation Platform includes a policy enforcement capability that controls what automation can do. When you combine this policy enforcement feature with Ansible Automation Platform’s robust automation foundation and its event-driven automation capability, you have a solid foundation for achieving visible governance, compliance, and an enhanced security posture. Especially in the age of AI, policy controls enable Ansible Automation Platform to be central to managing, governing, and controlling environments.
This covers the automation aspect, but defining the policies to enforce is equally important. Think of it this way: Policy as code is like a car, and the policy library is like the roads. You need both to get to where you're going.
So, what inflection points are appropriate for policy as code to assess code, environment, or configuration? Figure 1 provides an overview of common touchpoints with policy as code.

Figure 1: Policy as code provides controls and governance through the complete lifecycle of an environment.
Ansible Automation Platform is already part of your environment
If you're already running Ansible Automation Platform, policy as code is not a new tool, it's a new way to apply it to the compliance demands you face every day. Organizations often already orchestrate their infrastructure using playbooks and rulebooks. This means you're already collecting facts and audit trails of change over time through automation pipelines.
Administrators and AI solutions already have proper access to the systems they're allowed to act upon. Secrets management practices are already in place in automation to help protect sensitive data and technology. Policy enforcement is available in Ansible Automation Platform to further control what automation is allowed to do.
In contrast, dedicated compliance tools sit alongside your infrastructure—they observe it, report on it, and generate tickets someone else has to act on. We know Event-Driven Ansible makes automation immediately responsive to what's happening in the environment. Policy as code with Ansible Automation Platform provides the same bridge between automation and the visibility, management, and adherence to the complex world of security, compliance, and standards for your operational technologies.
In this model, you layer governance, compliance, and standards evaluation onto existing automation, making policies an extension of the automation you're already running.
You can extend benefits from automation to cover policy enforcement, evidence collection, compliance visibility, and remediation without adding new agents, new consoles, or new teams. The ability to remediate is already built into Ansible Automation Platform.
Compliance checks done your way
The ability to assess security posture in real time, catch configuration drift as it occurs, and build an audit trail helping demonstrate governance is transformative.
Most organizations operate between audit cycles—they know what their controls looked like last quarter, but may not know at the moment. Environments drift and change. It's common to complete an audit with a known-good state, and then experience drift and decline until the next audit.
Policy as code helps address this by providing a continuous picture based on structured, timestamped evidence. Drift events can be detected automatically, triggering event-driven automated remediation, which helps avoid finding issues during an audit. Because every result is stored historically, organizations can track compliance trends, demonstrate continuous improvement during audits, and identify which controls consistently fail. The combination of real-time visibility, drift control, and historical depth gives security teams a documented, continuous record of governance.
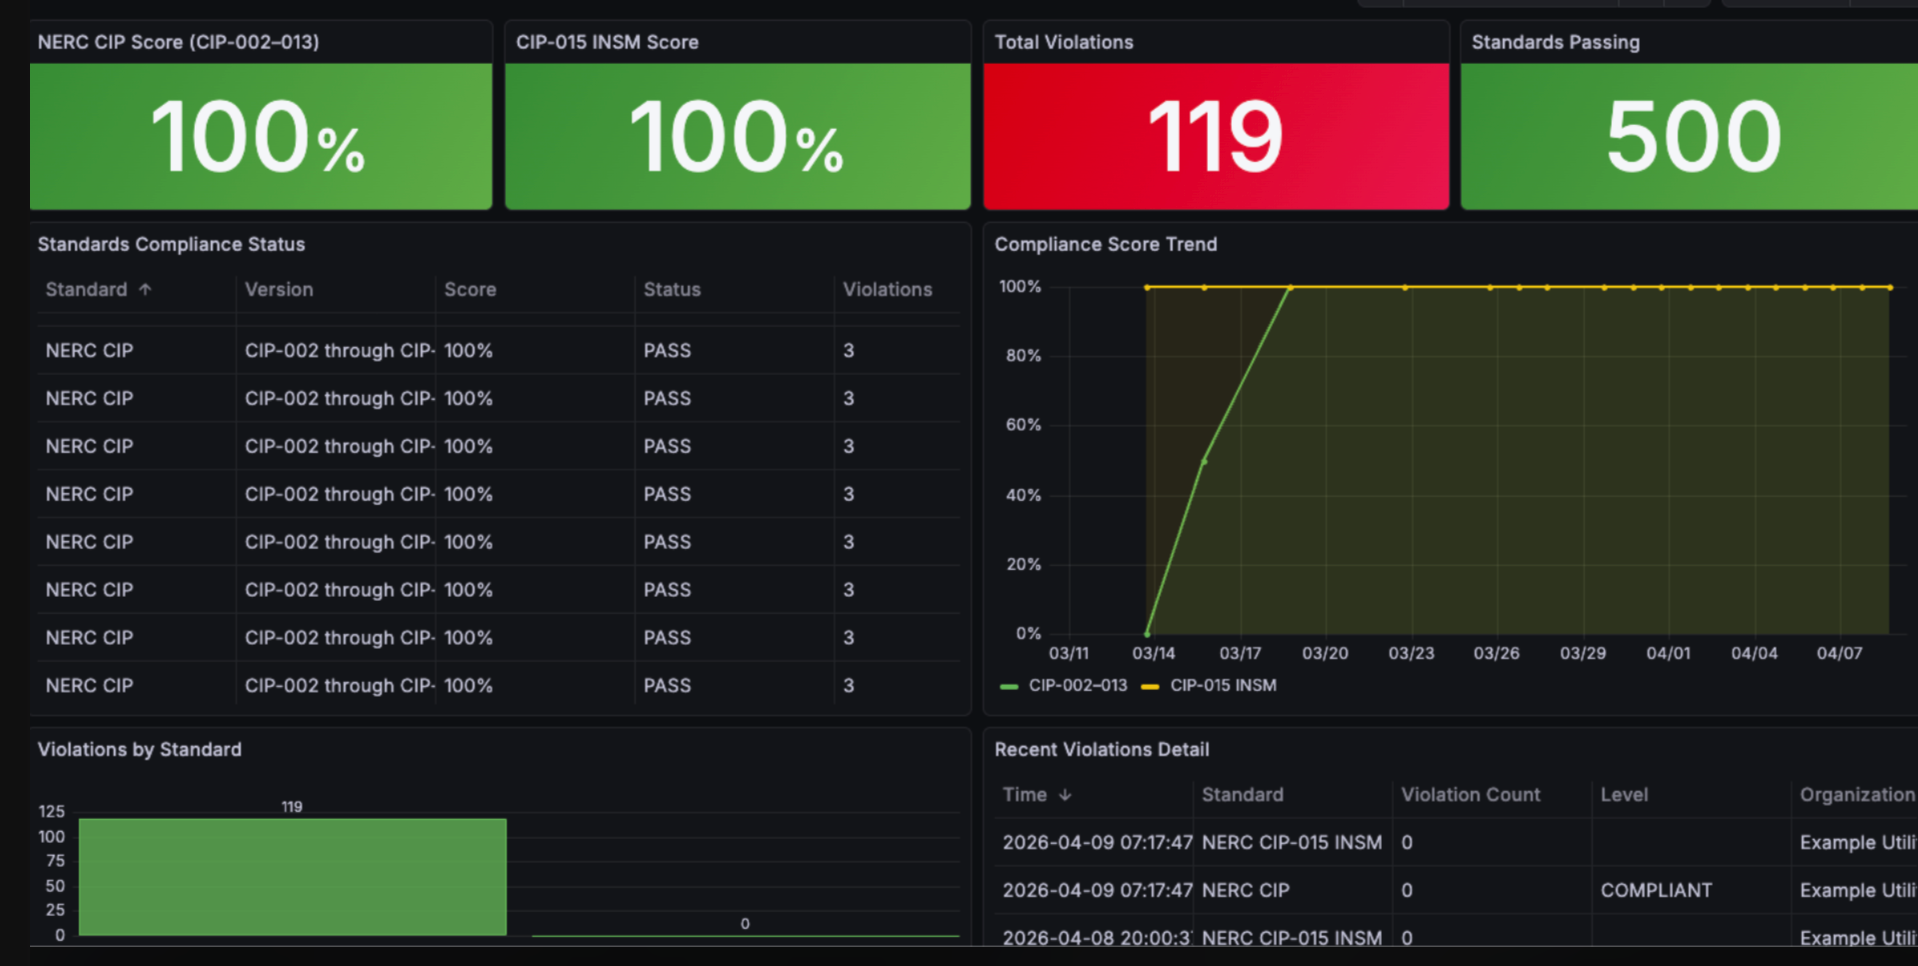
Figure 2: Real-time compliance reporting from a smart meter demonstration using Ansible Automation Platform and Grafana.
Applying policy as code
Ansible Automation Platform can help you automate enforcement of key compliance standards. You can define these standards using Open Policy Agent (OPA) Rego policies or even containerize them so they can be accessed and addressed as automation code.
Once policies are in place, you can automate and map them as structured policy evaluations before actions or automation can be completed. You can also generate compliance evidence automatically and store this information with timestamps, so when you're asked for documentation, the answer is a report pull, not a project.
There might be a gap between what's required and what's generated, since some compliance requirements include chain of custody and validated tools, but policy as code provides a continuous state and can be validated with other tools, like OpenSCAP.
Here are a few examples:
- Retailers and general business organizations must comply with a variety of regulations that focus on data protection, general IT practices, financial considerations, and privacy, such as:
- Payment Card Industry Data Security Standard (PCI-DSS)
- General Data Protection Regulation (GDPR)
- Center for Internet Security (CIS)
- Sarbanes-Oxley (SOX)
- System and Organization Controls 2 (SOC 2)
- ISO 27001
- Financial services organizations must address a range of standards that help protect financial infrastructure and systems worldwide, including:
- Digital Operational Resilience Act (DORA)
- ISO 22301 for resiliency
- SWIFT international payment mandates
- Gramm-Leach-Bliley Act (GLBA)
- Financial Conduct Authority / Prudential Regulation Authority (FCA/PRA) in the UK
- Utilities and grid operators must align with:
- North American Electric Reliability Corporation Critical Infrastructure Protection (NERC-CIP)
- Automated Metering Infrastructure (AMI2.0)
- Public sector organizations and providers may need to adhere to standards that govern a broad array of IT operations and cybersecurity, including:
- Federal Risk and Authorization Management Program (FedRAMP)
- Defense Information Systems Agency (DISA)
- Security Technical Implementation Guides (STIGs)
- National Institute of Standards and Technology (NIST)
- Healthcare and related organizations must comply with standards that govern data privacy, encryption, cybersecurity, and software development, such as:
- Health Insurance Portability and Accountability Act (HIPAA)
- Food and Drug Administration (FDA) regulations
- Other vendor-specific requirements for patient health records.
- Automotive and transportation organizations must demonstrate compliance with standards which focus on cybersecurity, risk management, and software development, such as:
- ISO/SAE 21434
- Software Process Improvement and Capability Determination (SPICE)
- Automotive Open System Architecture (AUTOSAR)
- and ISO 27001
- Telco, media, and entertainment companies must follow:
- ISO 27001
- Motion Picture Association (MPA) content security
- GDPR
- NIST, and others
- Industrial organizations must comply with:
- ISO/SAE 21434 for electronically secure automation and control systems
As you can see, many standards govern IT across industries and IT operations. No matter the standards impacting your organization, Ansible Automation Platform provides a flexible approach for codifying these standards as policies and automating their enforcement.
For demonstration purposes, this repository contains many examples of open source policies covering some of the most common compliance and security standards, written in Rego. You can explore using these as you set up automated policy as code.
Digital sovereignty: Compliance for a fragmented regulatory world
Let’s focus a little more deeply on digital sovereignty requirements, which are multiplying. They tie to GDPR mandates for data residency controls. DORA is a financial services mandate for Europe that includes digital sovereignty and operational resiliency aspects for financial supply chains. GAIA-X defines European data infrastructure standards. Information Security Registered Assessors Program (IRAP) governs the Australian government cloud. Network and Information Security 2 (NIS2) covers critical entity obligations across the EU. Each framework has its own controls, evidence requirements, and audit expectations.
Policy as code can be automated to assess your sovereignty posture across 11 domains in a single run, including:
- data residency
- cryptographic sovereignty
- infrastructure sovereignty
- software sovereignty
- operational sovereignty
- network sovereignty
- AI sovereignty
- breach notification
- geopolitical risk
- DORA resilience
- cyber resilience
The key is this assessment runs through the same Ansible Automation Platform workflows already managing the environment, without the need for a separate sovereignty monitoring agent, The difference is you'll include policy checks in the automation at key points across the workflow.
It's important to note policy enforcement in Ansible Automation Platform controls what automation can do, and you can include additional calls to policy checks to control actions in relation to your compliance mandates. The automation touching the infrastructure is the same automation generating compliance evidence through both reporting and audit trails.
AI governance: Enforcement that works today
AI governance is the fastest-moving regulatory frontier in the technology industry. The EU AI Act, emerging US frameworks, and sector-specific requirements are demanding auditability, access controls, and documented oversight of AI systems. Most organizations are trying to govern AI with processes designed for humans—manual reviews, after-the-fact logging, and policy documents.
By using policy as code, you can govern AI on an ongoing basis through the same automation layer that already exists in your environment. Every action an AI agent takes—every tool call, every data access, every model interaction—is evaluated against policies you designate before it executes. This helps you protect regulated data, block unauthorized actions, and automatically maintain structured audit records. You don’t need to build a separate AI governance stack, but rather extend what you already have.
Now let's look at some best practices and other considerations.
Collect continuous evidence
A snapshot of compliance may no longer be enough. In some areas, evidence of continuous compliance and operational resiliency are requirements where auditors want to see what's happening now. Ansible Automation Platform is already running, capturing audit trails of every action taken and allowing automated generation of current reports to satisfy these needs. Policy evaluation can be included in automation workflows for any IT process you desire.
Close blind spots with automation
Most security and compliance controls monitor what's running, not what's being deployed, and in the deployment phase policy exceptions are often introduced. By enforcing policies at every point throughout the orchestration process, you can close these gaps.
Simplify with a single platform
The compliance stack for most organizations is a collection of point solutions—for example, a cloud posture tool, a regulatory reporting tool, a vulnerability scanner, a configuration management database (CMDB), and an audit evidence system. Instead, policy as code lets you enforce policies through automation as you manage the environment. You can generate, post, or integrate compliance reports into your compliance database or dashboard.
Automate AI governance today
Every organization deploying AI faces the challenge of enforcing policies on solutions that move faster than governance processes. Policy as code evaluates AI actions against the same Rego policies from the same compliance database. It generates the same structured audit records as for any other infrastructure controls. As AI regulations mature, organizations using policy as code can already have the enforcement foundation that will be required.
Remediate non-compliance very quickly
Most compliance platforms find problems and create tickets. Next comes churn, where someone needs to read the ticket, open a change window, and schedule a fix. Multiple roles can be involved, so collaboration takes more time. Meanwhile, the non-compliant issue remains live. Using Event-Driven Ansible, you can implement an automated response, such as creating a ticket, triggering a backup, reapplying a security baseline, and updating a service ticket. The non-compliant issue is solved very quickly, often in seconds or minutes.
Embed compliance into automated processes from the start and throughout the operational lifecycle
Policy as code can be embedded into the automated processes your organization is already running. This extends the value of your existing Ansible Automation Platform investment and helps you deliver continuous evidence, drift control, and historical trending.
The combination of Ansible Automation Platform’s reach into infrastructure as a trusted automation solution and foundational Open Policy Agent (OPA)-based policies is what makes this work. Together, they enhance the automation layer with the ability to check for adherence to compliance and governance needs—a fundamentally different approach to a problem most organizations are still solving the hard, expensive, manual way.
Its value is in improving your compliance posture every day, enhancing efficiency and consistency, and helping you reduce the number of tools needed to perform compliance functions—all while allowing you to flexibly apply the standards that matter to your organization at scale.
An example demonstration including open source policies is available here.
Resource
5 steps to automate your business
About the author
Tim is a 5 year veteran of Red Hat, working as a Sales Solution Architect with some of our largest Customers, including major utility companies. He has focused on Automationas one of the initial drivers for the Policy as Code Solution at Red Hat. He also brings experience as a cloud Achitect, and Innovator, with 30demonstrated ability to deliver innovations and solutions to meet customer needs in the cloud, through automation and more.
More like this
Red Hat Ansible All-Stars: Driving the future of network and infrastructure automation
Closing the AIOps loop with Splunk Observability Cloud and Red Hat Ansible Automation Platform
Random Acts Of Automation | Compiler
Untangling Networks | Compiler
Keep exploring
- The automated enterprise
E-book - Try Red Hat Ansible Automation Platform with self-paced, hands-on labsInteractive lab
- Red Hat Ansible Automation Platform: A beginner’s guide
E-book
Browse by channel

Automation
The latest on IT automation for tech, teams, and environments

Artificial intelligence
Updates on the platforms that free customers to run AI workloads anywhere

Open hybrid cloud
Explore how we build a more flexible future with hybrid cloud

Security
The latest on how we reduce risks across environments and technologies

Edge computing
Updates on the platforms that simplify operations at the edge

Infrastructure
The latest on the world’s leading enterprise Linux platform

Applications
Inside our solutions to the toughest application challenges

Virtualization
The future of enterprise virtualization for your workloads on-premise or across clouds
